Access to Innovation
 Access to Capital
 Access to Talent
 Access to Market
 Access to Knowledge


From Cyber Threats to Industrial Resilience: Putting Security into Practice
Security Delta (HSD) aims to strengthen the cyber resilience of SMEs and organisations in essential sectors through a sector-based approach. The Cyber Resilience Centre Manufacturing South Holland (CWM), established by leading organisations in the manufacturing sector, is an example of this approach. By bringing together knowledge, expertise and practical experience, CWM translates this collaborative effort into tangible support to help manufacturing companies strengthen their cyber resilience.
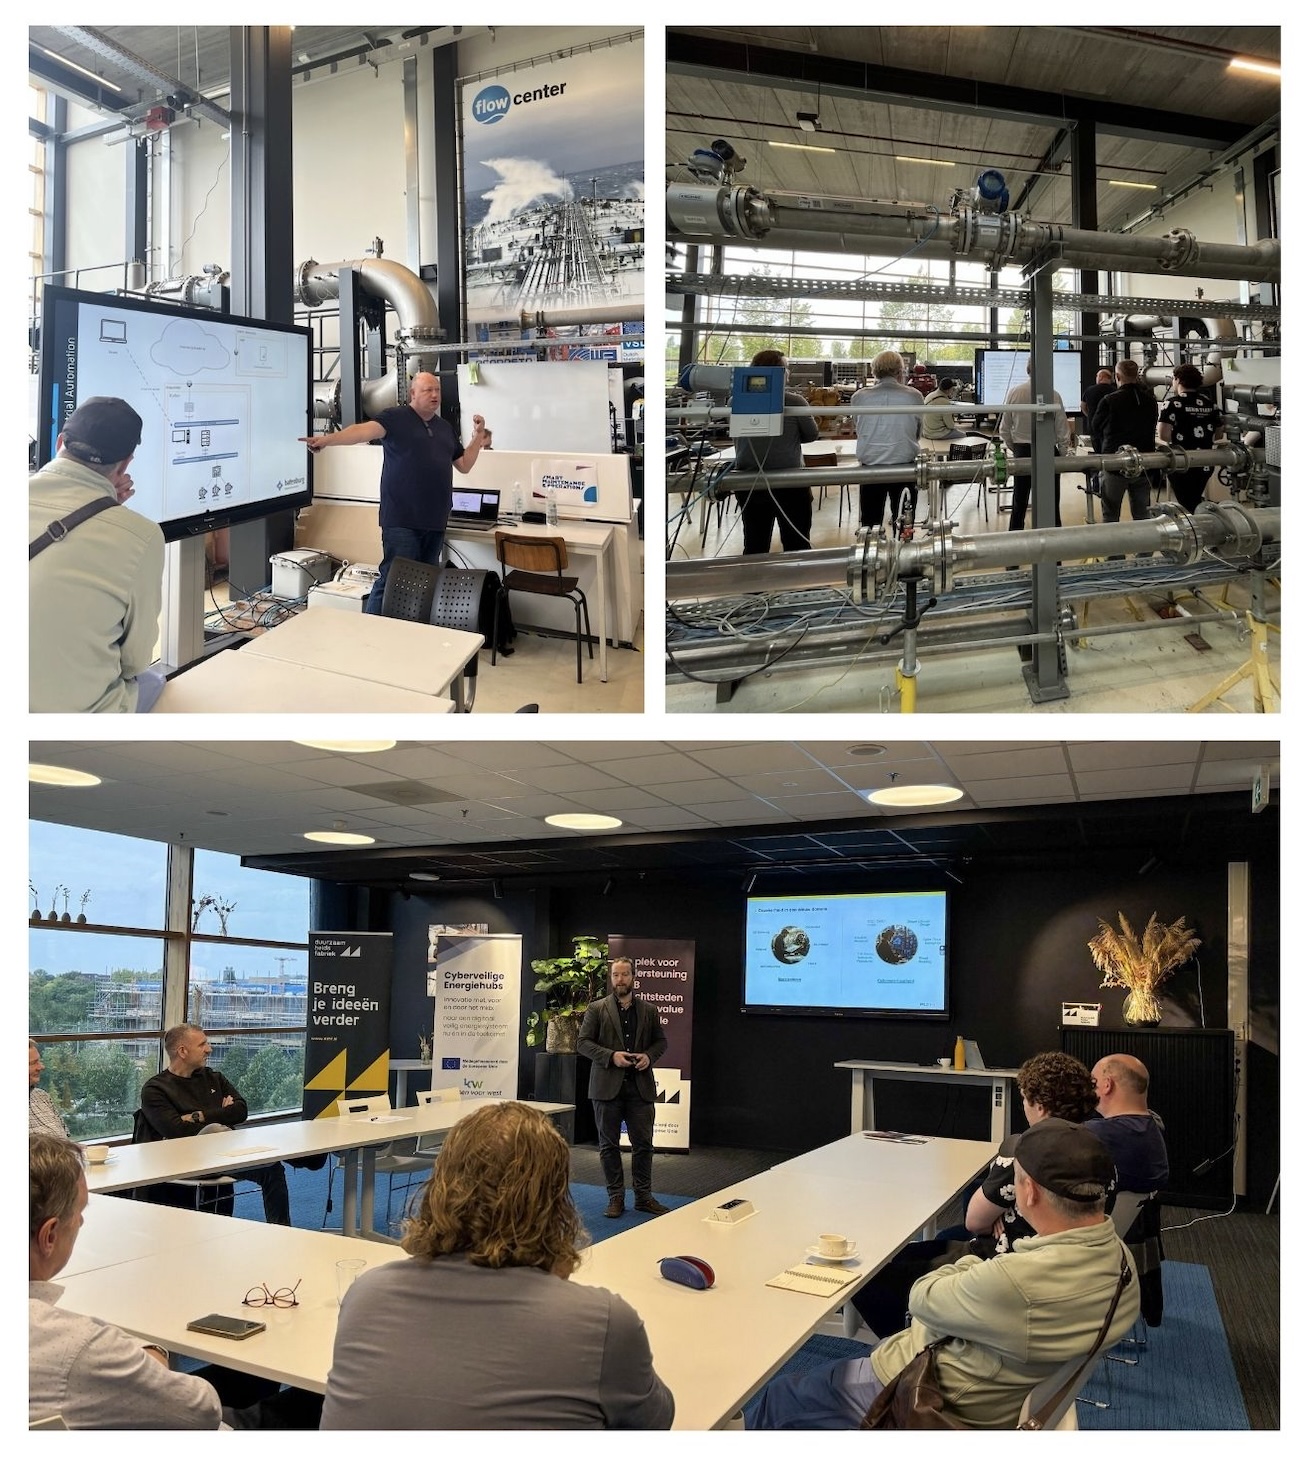
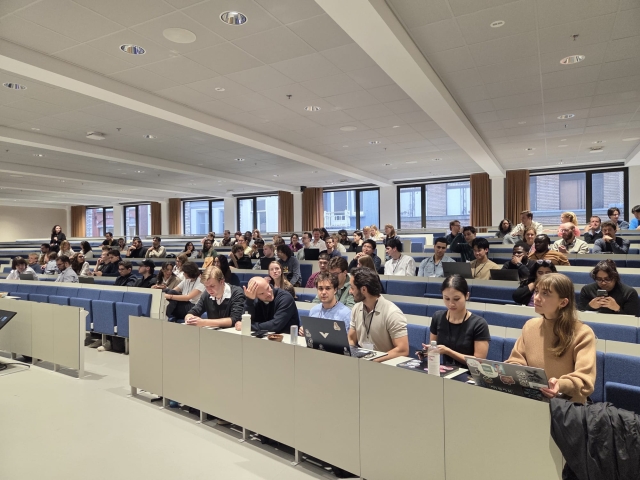
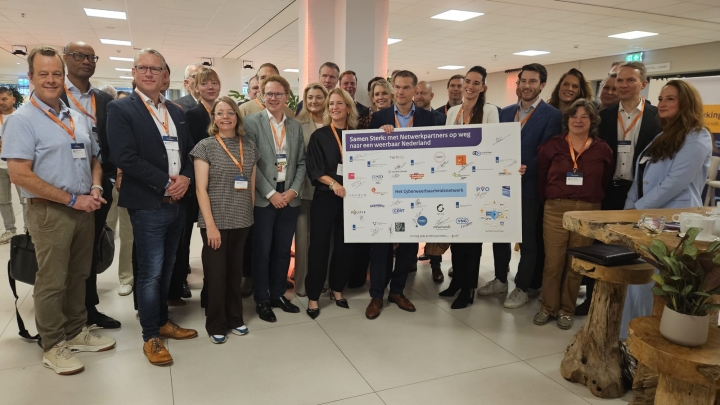
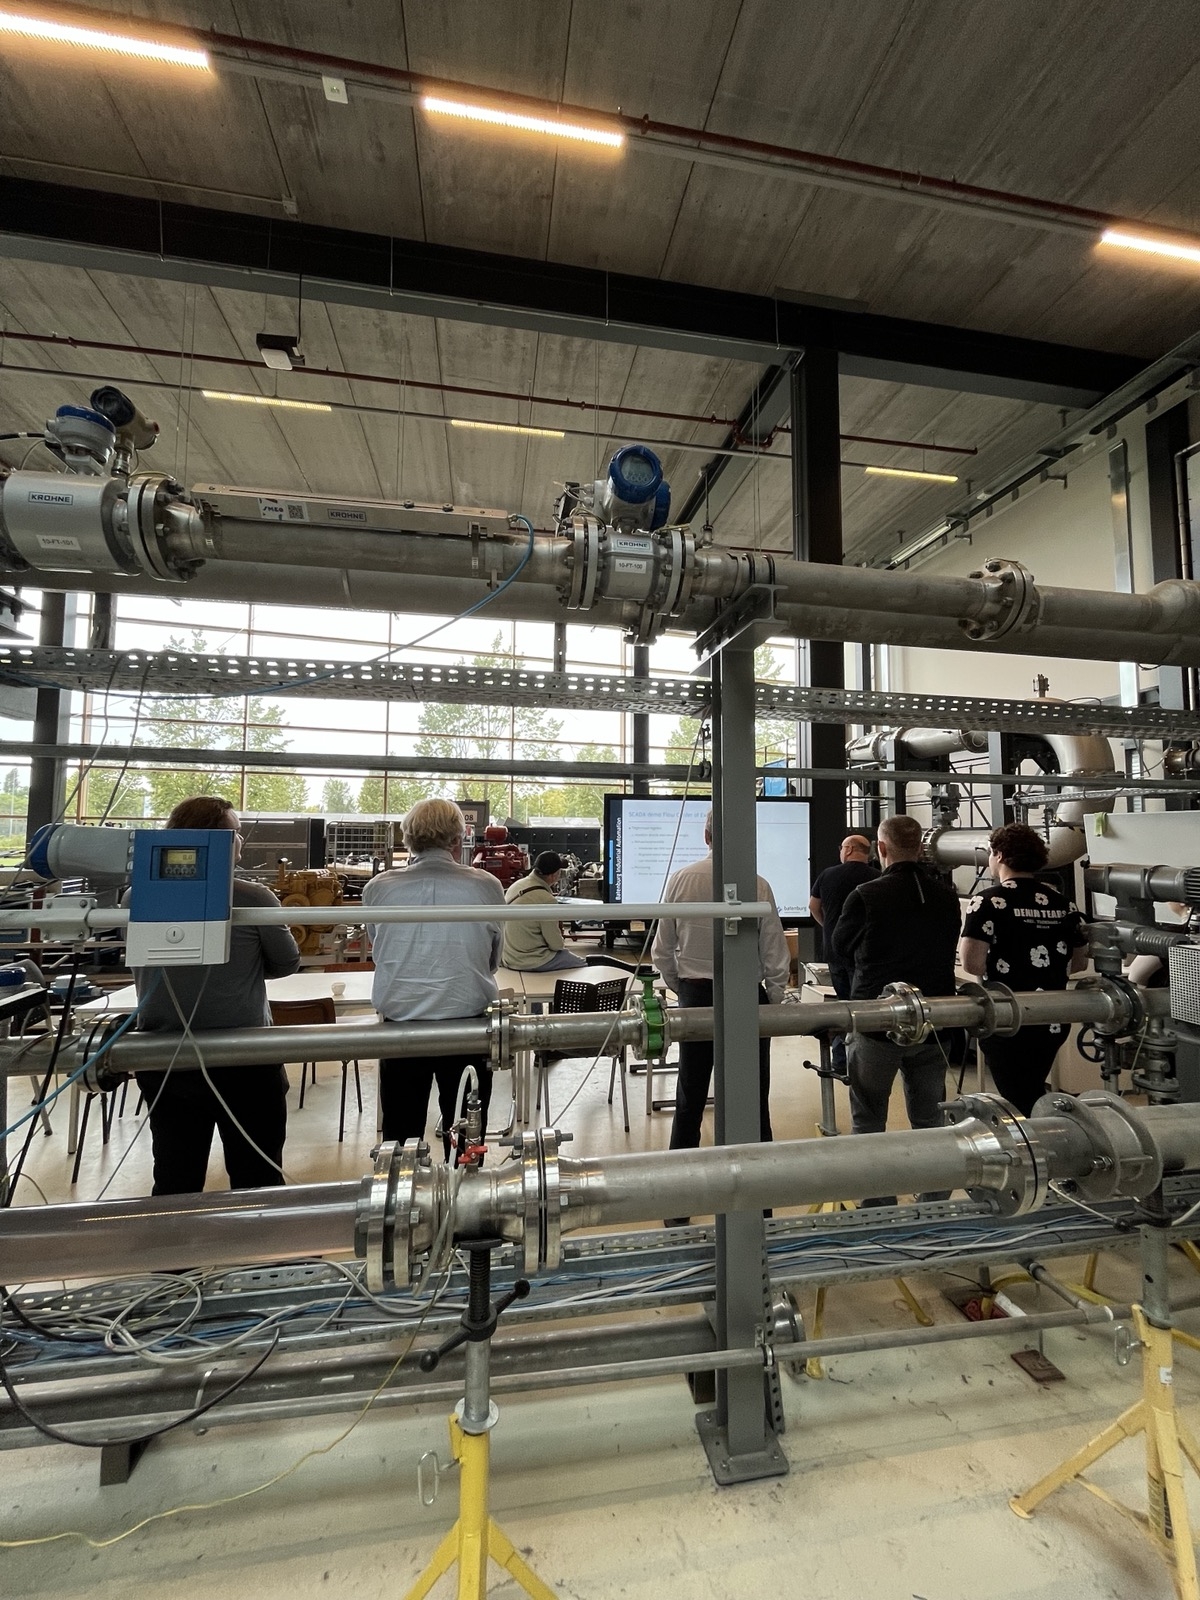
On 30 September, the event, ‘From Cyber Legislation to Security in Practice’, took place at the Duurzaamheidsfabriek in Dordrecht. Manufacturing companies gained insight into the risks of cyberattacks on industrial systems and the implications of European cybersecurity legislation, including the Cyber Resilience Act (CRA). A live hacking demonstration in the CWM OT Security Simulation and a presentation on legislation helped bridge the gap between theory and practice.
Live hacking demonstration highlights vulnerabilities in industrial systems
Rob Verseijden, an OT/ICS cybersecurity specialist at Batenburg Techniek, and a colleague demonstrated at the Flow Center of Excellence (FCoE) how an attacker could take control of the pumps in a test installation. Using a compromised operator workstation, they established a connection to an external server, enabling access to the industrial control system.
The demonstration made it clear that attacks do not always enter through the firewall. Systems that initiate connections to external servers can also pose a risk. Monitoring outbound network traffic and implementing network segmentation are therefore important measures for protecting industrial installations.
The human factor also played a role. Phishing emails, infected USB drives, AI-generated voice clones and deception involving physical access can all help attackers gain access to systems. Raising employee awareness is therefore an essential part of cybersecurity.
European legislation translated into practice
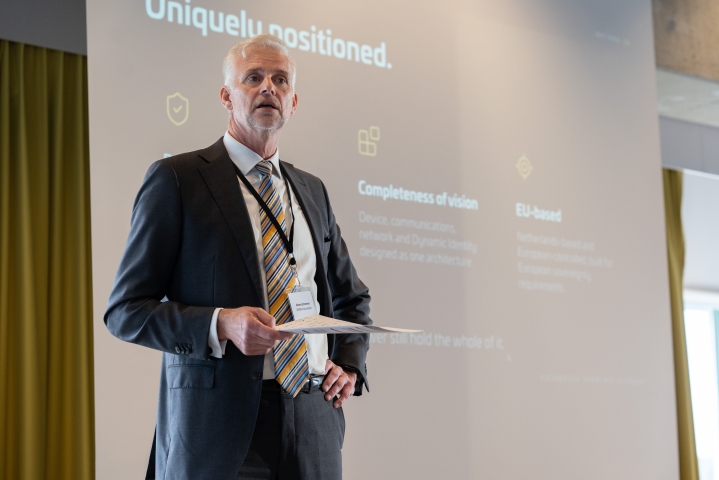
Mark Luchs, Industrial Security Consultant at Pilz, explained the NIS2 Directive, the Cyber Resilience Act (CRA) and the Machinery Regulation. He outlined what these regulatory frameworks mean for manufacturing companies, including the responsibilities they entail and the measures required to comply with them.
The event highlighted that cyber resilience requires a combination of technical security measures, clearly defined responsibilities and vigilance throughout the organisation.
The event was organised by Digitalzh, De Duurzaamheidsfabriek, Batenburg Techniek and the Cyber Resilience Centre Manufacturing South Holland.